Security Articles
12 articles on Security.
 Security alert
PHP2Shell: Two Critical PHP Flaws Hit Every WordPress and Laravel Site. Here's the Patch Plan
PHP shipped emergency fixes for CVE-2026-109618 and CVE-2026-109619 on October 21. Cloudflare's WAF rules help, but they are a stopgap. What agencies should do today.
 Security notice
WordPress 7.1.3 Security and Maintenance Release: What Agencies Need to Know
WordPress 7.1.3 fixes 7 security issues and 4 bugs. Here's what changed, how urgent the update really is, and how we handle it across client sites.
WordPress 7.1.1 Is Out: 11 Security Fixes and What Agencies Should Do Today
WordPress 7.1.1 landed September 17 with 11 security fixes and 36 bug patches. Here is our agency read on urgency, risk, and upgrade order.
Drupal SA-CORE-2026-013: The CKEditor 5 XSS, Who Is Actually Exposed, and How Fast to Patch
Drupal patched a moderately critical CKEditor 5 XSS on September 16. Anyone who can edit content can target your admins. Who is exposed, and how fast to move.
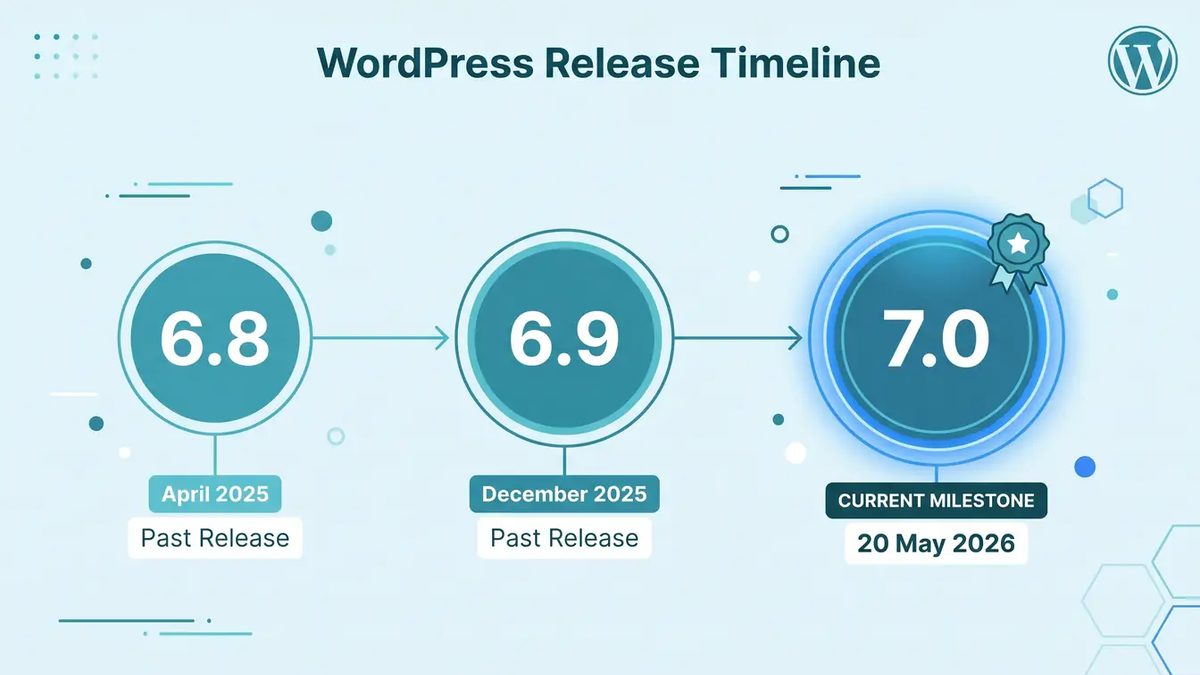
Four Patches in Six Weeks: What the WordPress 7.0 Cycle Taught Us About Update Discipline
WordPress shipped 7.0.1 through 7.0.4 between July 9 and August 12. Here's what that cadence revealed about our update runbooks, and what we changed.
WordPress 7.0.4 Security Release: What Agencies Need to Do This Week
WordPress 7.0.4 dropped August 12 with a security fix. Here's our read on urgency, client communication, and how to roll this out without drama.
WordPress 7.0.3 Security Release: What Agencies Need to Know Now
WordPress 7.0.3 is a security release. Here's what we know, how we're prioritizing client updates, and our practical checklist for patching safely.
Drupal's AI Security Initiative: What the First Six Weeks Tell Us
Drupal's new AI Security Initiative is six weeks old. Here's what's actually been built, what's still open, and what it means for agency Drupal projects.
WordPress 7.0.2 Security Release: What Agencies Need to Do Right Now
WordPress 7.0.2 patches one critical and one high severity security issue. Here's what we know, what we're doing for clients, and how to prioritize.
WordPress.org's New 24-Hour Plugin Release Cooldown: What It Means for Your Site
WordPress.org now holds all plugin and theme releases for 24 hours before auto-updates fire. Here's why it matters and what agencies should do now.

Composer 2.10 Ships Malware Blocking and Dependency Policies: What Laravel Agencies Need to Know
Composer 2.10 adds malware blocking for Packagist packages and a new dependency policy system. Here's what it means for Laravel agencies in production.
Drupal SA-CORE-2026-004: What Agencies Need to Know About the Critical SQL Injection
Drupal's security team patched a highly critical anonymous SQL injection in core on May 20. Here's our read on scope, urgency, and what to do now.